Hello colleagues,
I would appreciate your advice regarding PAM Segura implementation for Linux server access.
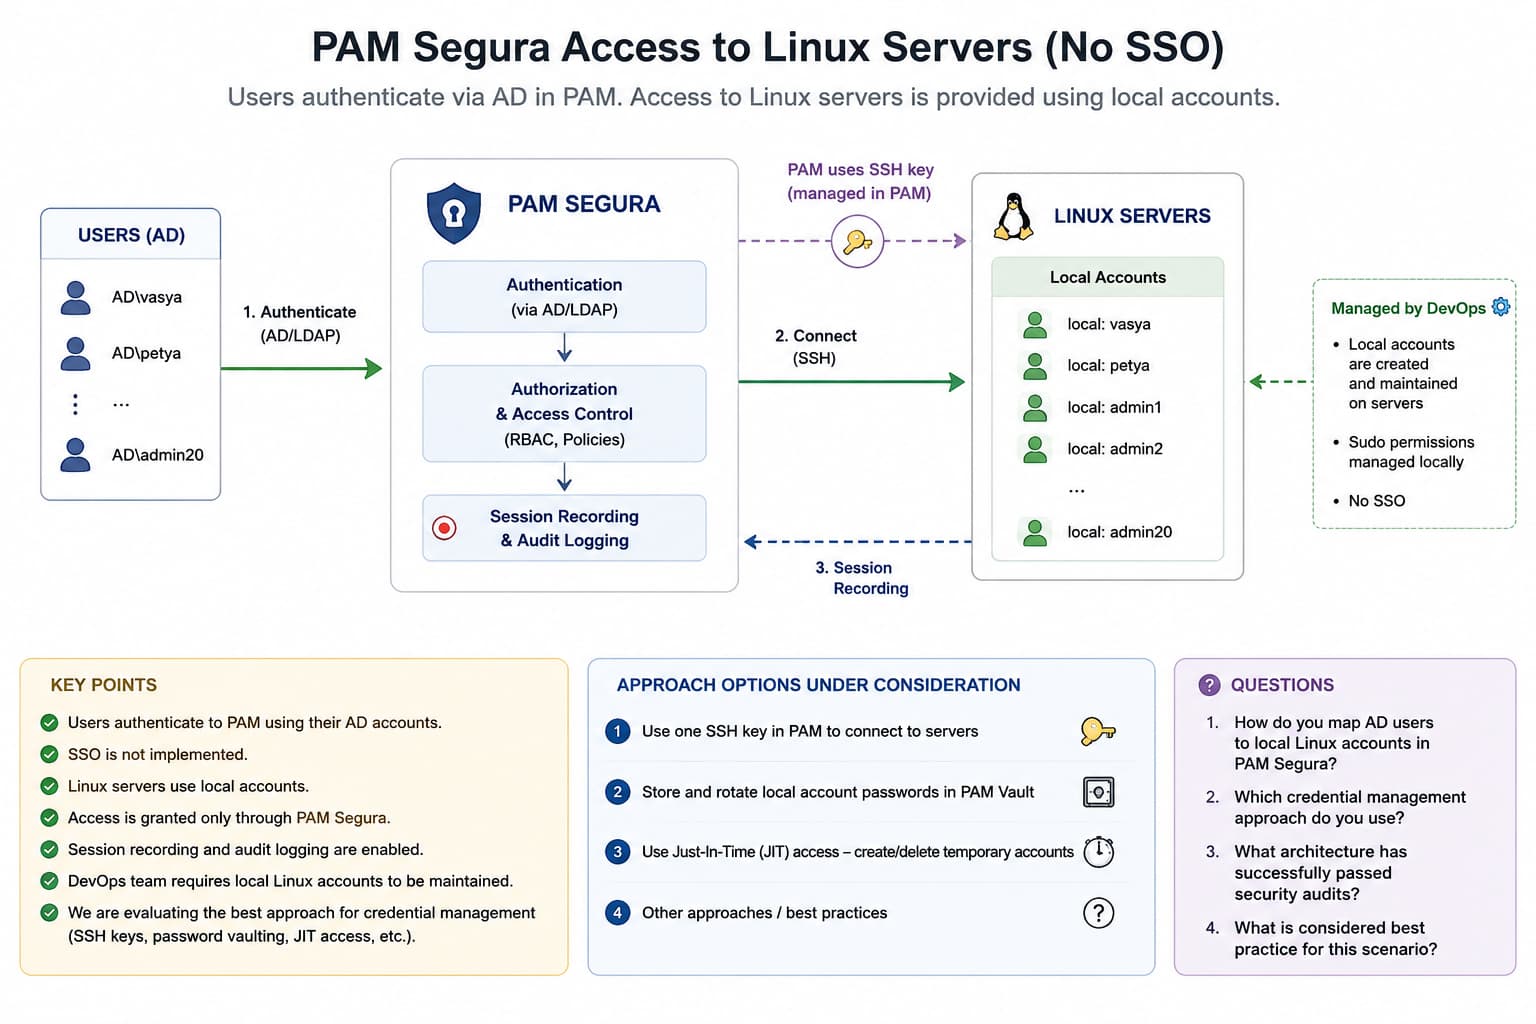
Currently, users authenticate to PAM through AD/LDAP, but SSO for Linux servers is not implemented and is not planned at this stage. Our DevOps team requires users to work with local accounts on the target Linux servers.
We are evaluating the following approach:
- Users authenticate to PAM using their AD accounts.
- Corresponding local accounts exist on Linux servers.
- Access to servers is granted only through PAM Segura.
- Session recording and audit logging are enabled.
- SSO is not being used.
We are trying to identify the most appropriate architecture from both security and operational perspectives.
We would appreciate hearing about your real-world experience:
- How do you map AD users to local Linux accounts when SSO is not available?
- Do you use shared SSH keys, individual credentials, or password vaulting for local accounts?
- How do you manage password or key rotation for local privileged accounts?
- Are you using Just-In-Time (JIT) access or temporary accounts?
- Which approach was accepted by your security team and successfully passed audits?
- What would you consider the recommended best practice for PAM Segura in this scenario?
Any recommendations, lessons learned, or implementation examples would be greatly appreciated.
Thank you in advance.